“Stop the Hackers, Lock Down the Side Doors” ... Government Makes Inspections Mandatory for All Systems Connected to Electronic Financial Services
- Input
- 2026-11-18 06:00:00
- Updated
- 2026-11-18 06:00:11
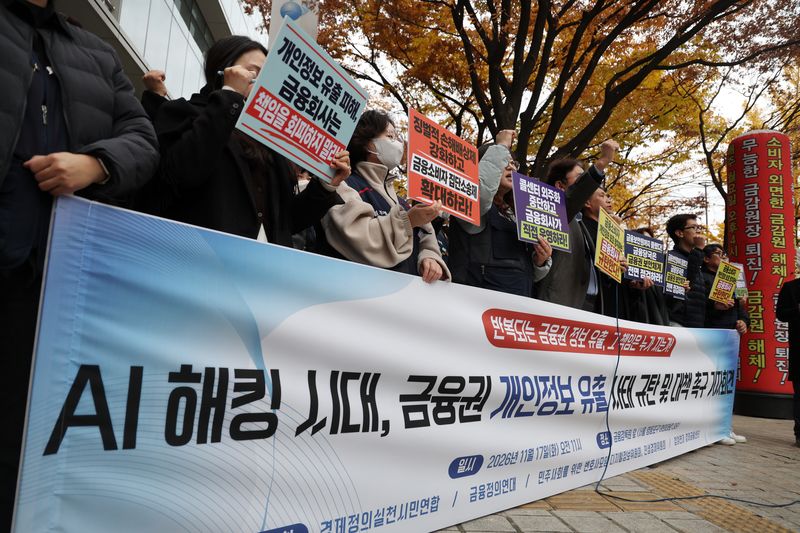
The Financial Services Commission (FSC) on the 18th disclosed a draft partial amendment to the Electronic Financial Supervisory Regulations and announced a proposed regulatory change. It is a follow-up measure to the FSC’s “Innovation Plan for Security Systems Across the Entire Financial Sector,” announced on the 5th.
The expanded inspection frequency will apply to large financial companies with total assets of at least 2 trillion won and at least 300 full-time employees. These companies will have to conduct vulnerability analyses and assessments once every six months, or twice a year. The FSC plans to apply the requirement first to large financial firms with the capacity to conduct the checks, then rapidly expand its scope after reviewing the financial sector’s preparedness.
Under the Electronic Financial Transactions Act, vulnerability analysis and assessment is a process in which financial companies and electronic financial business operators use the Financial Security Institute, private security firms, or other providers to identify vulnerabilities in their IT assets and submit the results and plans for remediation to the financial authorities. The amendment sets not only the frequency of checks but also the scope that must be examined. All information-processing systems used in direct or indirect connection with electronic financial infrastructure will be included in the checks.
Until now, regulations had not defined the scope of mandatory checks, and there were many cases in which companies focused on core systems and overlooked peripheral ones. Recent hacking incidents in the financial sector have also occurred mainly in peripheral systems, such as business support management systems, which are relatively vulnerable, rather than core systems with strict security management. The aim is to prevent a recurrence of information leaks caused by hacking by checking vulnerabilities in these so-called “side doors,” too. The FSC expects attacks using AI to continue targeting vulnerable points like “side doors” quickly and meticulously.
The IT asset management requirement will apply to all financial companies and electronic financial business operators covered by the Electronic Financial Transactions Act. Each company will have to identify all of its information technology assets, including information-processing systems, communications equipment, and information security systems. They must classify the importance of each asset, designate a person responsible for it, and keep the inventory up to date.
A basis will also be established for the Financial Services Commission to require ad hoc inspections in emergencies. Such cases include similar breaches occurring in succession at multiple financial companies or the discovery of a critical vulnerability in widely used software such as PHP. The plan is for the financial company or electronic financial business operator concerned to conduct vulnerability analyses and assessments without delay once the financial authorities specify and notify them of the targets and scope.
The FSC plans to implement the amendments by the first quarter of 2027. After the advance notice of the proposed regulatory change, the process will include reviews by the Ministry of Government Legislation and the Regulatory Reform Committee, as well as an FSC resolution. In view of the time needed to amend the regulations, the FSC will first pursue the increased inspection frequency for large financial firms and checks of all connected systems through administrative guidance. The guidance is not legally binding, but the FSC expects the financial sector to comply voluntarily.
After a five-day period for comments from today through the 23rd, the administrative guidance is scheduled to undergo deliberation and a vote by the FSC’s Financial Administrative Guidance Deliberation Committee. It is tentatively set to take effect on the 30th and will remain in force until the regulations are amended.
[email protected] Park Mun-su Reporter