Raven Enters South Korea’s Security Market, Tackling AI-Powered Vulnerability Attacks
- Input
- 2026-11-12 14:53:00
- Updated
- 2026-11-12 14:53:04
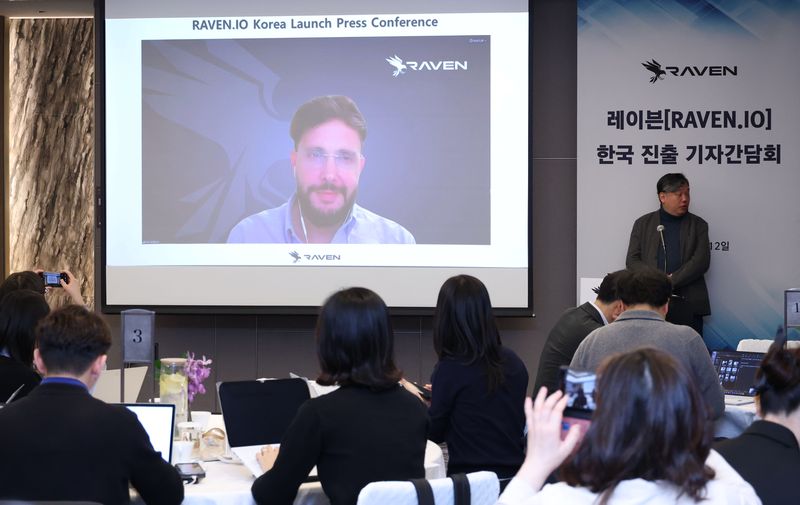
Countering AI-Driven Vulnerability Attacks...Blocking Them at Runtime
Raven held its first press conference in South Korea on the 12th at JW Marriott Hotel Seoul in Seocho District, Seoul, where it introduced its strategy for entering the Korean market and its application security technology.Raven is targeting financial institutions and companies in Korea in partnership with Singapore-based business consulting firm The Executive Action. According to the company, just three months after entering the Korean market, it is already working with major financial institutions and companies in the country.
Raven’s core technology is “runtime security,” which protects applications while they are running. Whereas conventional security methods have focused on responding to publicly disclosed vulnerabilities or known types of attacks, Raven focuses on detecting and blocking abnormal behavior as programs actually run.
As more attackers use AI to analyze and exploit software vulnerabilities, the limitations of existing security systems are becoming more apparent. In particular, vulnerabilities in open-source software widely used by companies can affect multiple systems when discovered.
Raven’s technology analyzes an application’s internal libraries, functions and execution paths to identify abnormal behavior. Rather than relying solely on publicly disclosed vulnerability information (CVE) or existing attack patterns, it is designed to analyze how programs actually behave at runtime and block attacks.
Raven co-founder and CEO Roi Abitboul said, “Companies cannot rely on a model in which they begin protecting themselves only after a CVE is disclosed. Security teams need to understand what code does while it is running and be able to block exploitation even when there are no known vulnerabilities or attack patterns.”
Targeting Regulated Industries Such as Finance...Expanding Partnerships in Korea
Raven has identified regulated industries that handle sensitive information, including finance, as key targets for its business in Korea. The company says these industries place great importance on protecting personal information and ensuring service continuity, while the complex interconnections among multiple operating systems and applications create a significant security management burden.Raven plans to address the security needs of individual companies with runtime protection technology that supports a range of operating systems and programming languages. The Executive Action will identify the requirements of Korean companies and support them in evaluating and adopting the technology.
Adrian Ong, managing director of The Executive Action, said, “Korean companies need protection systems that take into account the complexity of their existing application environments. We will work with various organizations in Korea to help them evaluate and adopt Raven’s runtime protection technology.”
[email protected] Yoon Hong-jip Reporter