“His face has been made public, yet he still hasn’t been caught after 8 years” ... North Korean hacker Park Jin Hyok, whose good looks left even the U.S. FBI stunned
- Input
- 2026-11-10 05:10:00
- Updated
- 2026-11-10 05:10:00
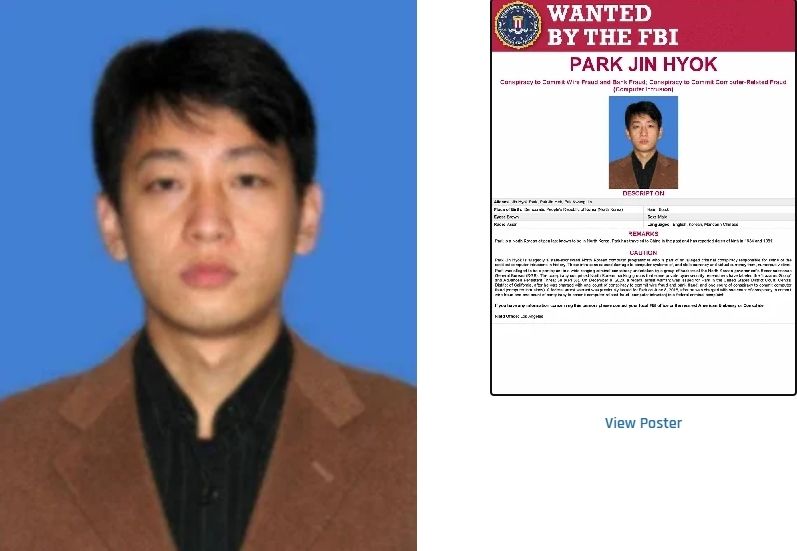
[Financial News] A North Korea-linked group has been named as being behind the largest-ever hacking incident, worth around 8 trillion won, at Binance, the world’s largest cryptocurrency exchange. This has once again drawn international attention to North Korean hacker Park Jin Hyok, who has been on the FBI’s wanted list for eight years.
₩8.4 trillion vanishes from Binance ... Lazarus-linked forces behind the attack
According to publicly released U.S. FBI information and foreign media reports on the 9th (local time), the FBI identified North Korean cyberattack group TraderTraitor as responsible for the theft of cryptocurrency from Binance that occurred on the 31st of last month.
The cryptocurrency stolen in the attack, carried out on the 29th of last month, was worth about $6.3 billion (about 8.4 trillion won). TraderTraitor is an organization officially identified by the U.S. Cybersecurity and Infrastructure Security Agency (CISA), the Treasury Department and others as linked to the Lazarus Group, a key hacking organization within North Korea’s Reconnaissance General Bureau (RGB). The incident has once again brought to light the activities of North Korean operative Park Jin Hyok, a key member of the Lazarus Group and the first North Korean agent to be indicted by U.S. law enforcement.
From Sony Pictures Entertainment to WannaCry ... at the forefront of state-backed cyberterrorism
Park Jin Hyok was the first person to be criminally indicted by the U.S. government on charges related to a major North Korean cyberattack. The U.S. Department of Justice obtained its first arrest warrant in June 2018, then made public a complaint that September detailing charges including computer fraud and abuse, officially identifying him.
According to U.S. investigators, Park Jin Hyok was at the center of major state-backed cyberattacks that shook the world. It began with the 2014 Sony Pictures Entertainment hack. Ahead of the release of the film The Interview, which dealt with the assassination of North Korean leader Kim Jong Un, Park infiltrated the company’s computer network, destroyed systems, leaked large amounts of employees’ personal information and unreleased films, and carried out a retaliatory attack.
In 2016, he broke into Bangladesh Bank’s computer network and manipulated SWIFT codes. After attempting fraudulent transfers of about $1 billion targeting the Federal Reserve Bank of New York, he stole $81 million (about 110 billion won), shocking the international financial sector.
The following year, in 2017, he was also deeply involved in the distribution of the WannaCry ransomware, the worst such ransomware incident ever, which paralyzed computer networks at hospitals, financial institutions and public agencies in some 150 countries around the world at once.
His activities, which spanned cyberterrorism and financial extortion, continued. In February 2021, the U.S. Department of Justice brought additional charges against three programmers from North Korea’s Reconnaissance General Bureau, including Park Jin Hyok, Jeon Chang-hyok and Kim Il, alleging that they targeted financial institutions and companies around the world and attempted to steal or extort at least $1.3 billion (about 1.7 trillion won) in total, tightening the net around them.
Operating overseas bases through front companies ... still difficult to take him into custody after 8 years of pursuit
According to investigative records, Park Jin Hyok graduated from Kim Chaek University of Technology, North Korea’s most prestigious science and engineering university, and worked for more than 10 years as a programmer at Chosun Expo Joint Venture, a front company for earning foreign currency under the RGB’s 110th Research Center. He was found to have operated from overseas bases, including Dalian in Liaoning Province, China, carrying out large-scale malware development and cyber operations under the guise of legitimate outsourced software development.
The FBI has published detailed information on its cyber wanted list, including his photo and fingerprints, aliases he used (such as Park Kwang-jin), his ability to speak English and Chinese, and the birth years listed as 1981 and 1984, and continues to pursue him. The Australian government also placed Park Jin Hyok on its own financial sanctions list last year and banned him from entering the country.
However, as his last known whereabouts are believed to be inside North Korea, he has still not been physically apprehended, even eight years later, in part because there is no extradition treaty with the United States.
North Korea flatly denies the allegations as “a baseless fabrication”
The North Korean regime strongly denies allegations of its involvement. When the United States indicted Park Jin Hyok in 2018, North Korea responded in a statement by a Foreign Ministry official, calling it “a U.S. smear campaign against North Korea, parading a person who does not even exist.”
Regarding the Binance hacking incident, involving around 8 trillion won, Kim Yo Jong, vice department director of the Workers’ Party of Korea, issued a statement on the 3rd and flatly denied the allegations, saying, “The United States is unjustifiably linking international cybercrime cases to us.”
[email protected] Mun Yeong-jin Reporter