'473,000 Data Records Exposed Across Financial Sector' ... Lee Eog-weon: “Security Lapses Are Management Failures ... I Will Hold Executives Accountable”
- Input
- 2026-11-05 10:35:15
- Updated
- 2026-11-05 10:35:15
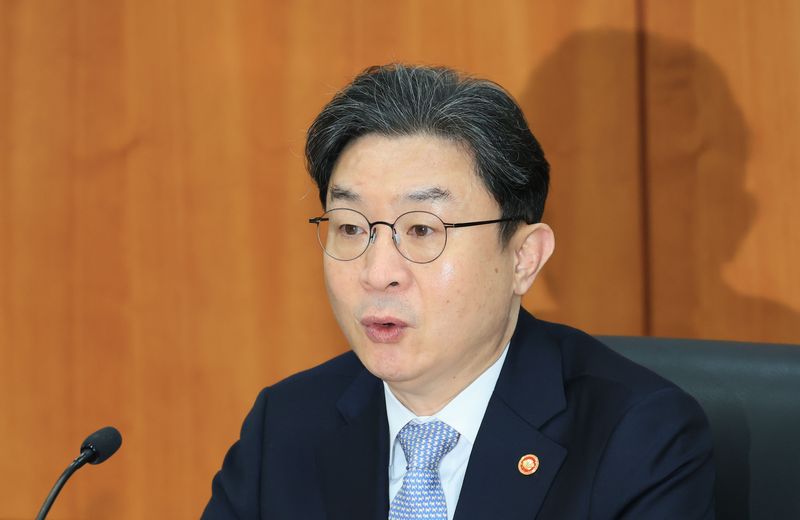
“Serious Failures: We Will Hold CEOs Accountable”
Financial Services Commission Chairman Lee Eog-weon held a meeting on the 5th at the Yeouido branch of the Financial Security Institute in Yeongdeungpo District, Seoul, with the Financial Supervisory Service, the Financial Security Institute, heads of associations across the financial sector—including those representing virtual asset, electronic finance, and online investment-linked finance businesses—and relevant government ministries. He said, “For serious failures in security management or negligence in responding, we will strictly hold management, including chief executive officers (CEOs), accountable under relevant laws,” and warned that “failures in security management can lead beyond mere technical failures to failures in management.”He added, “A financial company that cannot protect its customers’ information and assets has already lost its reason to exist,” and called on “CEOs across the financial sector to immediately form company-wide emergency response teams.”
According to the Financial Services Commission, beginning with Shinhan Bank, which confirmed the leak of 25,000 customer records on September 30, there were 40 reports of cyber breaches at a total of 37 financial firms over roughly a month, through the 3rd of this month. They included 4 banks, 5 financial investment firms, 3 insurers, 5 savings banks, 1 mutual finance institution, 2 credit finance firms, 4 online investment-linked finance firms, 10 electronic finance businesses, and 3 virtual asset firms.
All 580 Financial Firms to Undergo Comprehensive Inspections
The financial authorities plan to swiftly complete comprehensive security inspections at around 580 firms, covering not only banks, securities firms and insurers but also the virtual asset sector. They have set a deadline of the 30th of this month for systems listed in the management registers, and the end of next month for inspections to be completed, including for unlisted systems.They will also inspect how financial firms’ chief executive officers (CEOs), chief information security officers (CISOs), chief information officers (CIOs) and others are operating internal controls. The authorities plan to take strict measures if any cyber breach occurs after these comprehensive inspections.
The authorities plan to upgrade the Integrated Monitoring System (FIRST), the financial sector’s joint cyberattack monitoring system, begin pilot operations next month, and make it available to the entire financial sector in the first quarter of next year. They will also begin piloting an AI-based “suspicious transaction assessment index” this month.
The authorities also plan to step up efforts to ease network separation regulations by launching in earnest this month a task force to fully lift those regulations and build an AI-based security system. They will also prepare the Digital Financial Security Act in the first quarter of next year to establish rules for IT security. In addition, they plan to actively support the enactment of amendments to the Special Act on the Prevention of Loss Caused by Telecommunications-Based Financial Fraud and Refund, introducing a no-fault liability system under which financial firms compensate victims for a portion of their voice-phishing losses.
[email protected] Jo Eun-hyo Reporter