Lee Chan-jin says he will hold securities and insurance CEOs accountable for hacking incidents
- Input
- 2026-11-03 15:36:46
- Updated
- 2026-11-03 15:36:46
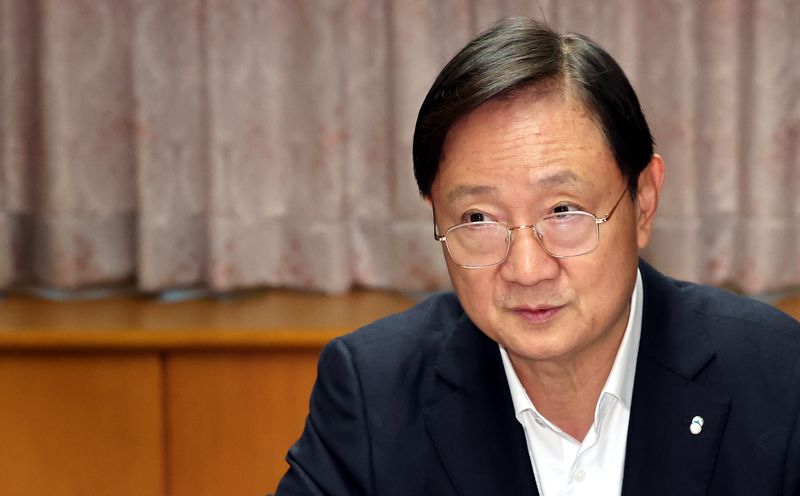
[Financial News] On the 3rd, Financial Supervisory Service Governor Lee Chan-jin said, regarding recent hacking incidents, “I will hold the CEOs and other executives of large securities firms and insurance companies accountable.” He also said, “I will actively engage with the National Assembly to secure passage of an amendment to the Electronic Financial Transactions Act so that punitive surcharges of 3% of revenue can be imposed without exception when hacking incidents occur due to inadequate basic controls, unaddressed security vulnerabilities, or similar failures.”
According to the FSS, Lee stressed at an executives’ meeting that morning, “Even though we instructed financial institutions to block external access in principle, except where absolutely necessary, immediately after cyber incidents began to escalate, the financial sector’s compliance was insufficient.”
This is the second time Lee has stated that he will hold financial companies’ CEOs accountable in the event of information leaks. At a National Assembly audit by the National Policy Committee on the 19th of last month, when reports of hacking damage at commercial banks and savings banks were concentrated, he said, “For the first time in a financial-sector cybersecurity hacking incident, the issue of CEO accountability will be addressed.”
Lee said, “Ensuring IT security is the foundation of customer trust and a key survival strategy,” and urged them to expand security budgets and staffing next year. He also called for the creation of a dedicated security unit and an increase in specialist staff so that effective supervision and inspections can be carried out to strengthen IT security across the financial sector. He said punitive surcharges for information leaks in the financial sector would be introduced swiftly, and that he would explore various measures to promote stronger security, including levying supervisory contributions at differentiated rates.
Lee also called for financial institutions across the sector to conduct their own IT checks to prevent further information leaks, including firms not covered by the Electronic Financial Transactions Act, such as corporate insurance agencies (GAs). Reviews of the sector-wide self-checklists completed by the 8th of last month found that about 100,000 records of personal information had been leaked at 16 companies. Reports of cyber incidents have continued to come in from insurers and securities firms since then. Financial losses have also occurred in the virtual asset and online investment-linked finance industries.
[email protected] Jo Eun-hyo Reporter