Lee Chan-jin: “Internal control guidelines have limits in addressing IT errors ... Will discuss improvements with the FSC”
- Input
- 2026-10-19 15:06:31
- Updated
- 2026-10-19 15:06:31
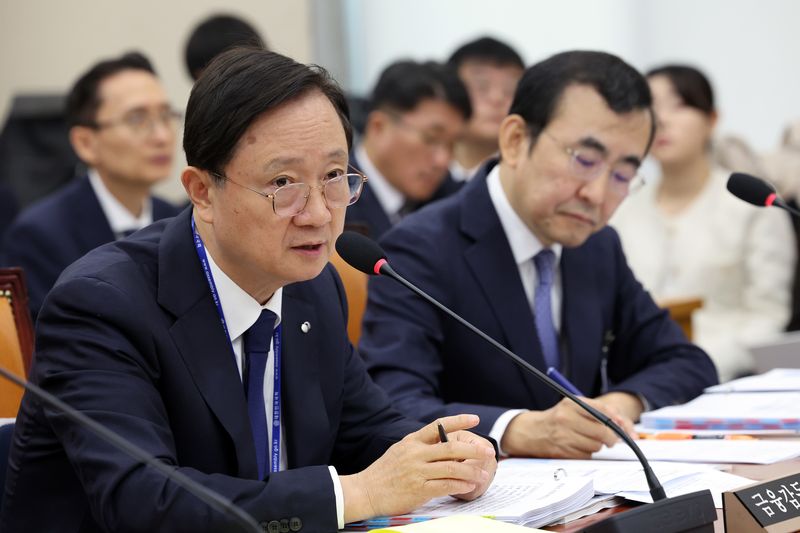
At a parliamentary audit of the Financial Supervisory Service and other agencies by the National Assembly’s National Policy Committee on the morning of the 19th, Governor Lee responded to Rep. Kim Hyeong-yeon of the Rebuilding Korea Party, who called for improvements to the response system for internal IT incidents. “We are identifying vulnerabilities related to system failures,” he said, adding, “It seems difficult to ensure that internal controls are properly implemented under the current guidelines.”
He added, “As we pursue the Digital Asset Basic Act and work to amend the Electronic Financial Transactions Act, I will discuss with the FSC ways to address this issue as well.”
In his questioning that day, Rep. Kim pointed to cases in which financial companies had failed to detect errors in their internal systems for extended periods.
According to materials released by Rep. Kim, it took Lotte Insurance 902 days and Toss Bank 670 days to discover software errors. There were nine cases at Toss Bank in which incident detection was delayed by 30 days or more, and seven each at Suhyup Bank and KB Kookmin Bank. In other words, the same financial companies repeatedly discovered errors late.
Rep. Kim specifically cited currency exchange and remittance errors at Toss Bank, saying that internal system failures can also result in direct financial losses. In March, Toss Bank canceled all currency exchange transactions worth 27.6 billion won after an error occurred in its yen-to-won exchange-rate quotation system. On the 7th of this month, another error caused a transaction processed as a failed remittance by another bank to be recorded as a deposit into a Toss Bank account.
Rep. Kim said, “Although attention has recently focused on hacking and personal information leaks, preventing and detecting internal system errors and taking follow-up action are just as important as they are for hacking.”
Rep. Kim also called on the Financial Supervisory Service to improve the financial security management framework announced by the FSC on the 14th, saying, “It focuses only on responding to hacking and managing security vulnerabilities, and leaves out measures to verify internal IT systems for errors in advance and detect them early.” There were also calls to review the causes and whether improvements had been made at financial companies where delays in detecting incidents had recurred.
The enforcement gap for reporting obligations involving internal IT incidents was also raised. Under the Electronic Financial Transactions Act, financial companies must notify the FSC within 24 hours when an external intrusion incident occurs, and failure to do so can result in a fine of up to 10 million won. Ordinary electronic financial incidents, by contrast, are covered by the Electronic Financial Supervisory Regulations rather than by law, meaning there is no legal basis for imposing a fine even when the rules are violated.
Asked why a draft amendment to the relevant enforcement decree, which the FSC had put out for public notice in 2024, had not led to an actual amendment, Governor Lee replied, “I will look into it.”
[email protected] Lee Hyun-jung Reporter