SNS users buying up Upbit API keys, saying “It’s only for viewing” ... “A sign of fraud” [Crypto Briefing]
- Input
- 2026-10-08 08:58:05
- Updated
- 2026-10-08 08:58:05
[Financial News] Offers to buy authentication keys while claiming they are needed to view data that requires no authentication are on the rise on social media. Upbit’s price and market data are public information that anyone can access without a key. Yet the claim that accounts and application programming interface (API) keys are being bought “for viewing only” makes no sense. This contradiction itself, observers say, is the clearest warning sign. On the 8th, Dunamu Inc., operator of the digital asset exchange Upbit, urged investors to exercise particular caution over messages requesting to “borrow API keys and accounts,” which have recently spread mainly on social media.
Open API key security guidelines
Numerous cases have been spotted on social media of people approaching investors and saying they will rent or buy Upbit accounts that can access the KRW market, or API keys with read-only or viewing-only permissions. They try to reassure investors, claiming they will “never make deposits, withdrawals or trades, and will use the keys legally only to view market data.” But the requests themselves are false. Upbit’s standard price and market data (Quotation API) are available through a public API that requires no authentication. If an API key is leaked, it could be used for fraud or other unauthorized purposes, leading to financial losses.
Dunamu Inc. strongly warned that accounts must not be lent to others, or open API keys (Access Key, Secret Key) provided to them, for any reason. API keys are important authentication credentials that, depending on the permissions granted, can be used to view members’ asset, order, deposit and withdrawal information or access trading functions.
Anyone who obtains Upbit login credentials could misuse them and cause severe harm, including the theft of assets. Members are responsible for all financial losses resulting from careless handling of personal information and API keys, or lending them to others, so they should be especially cautious.
To protect assets, Dunamu Inc. urged members to follow its “Open API Key Security Guidelines” carefully. First, do not share API keys or account information with others. Never disclose or leak information such as an Access Key or Secret Key for any purpose. If an API key has been exposed or is suspected of being leaked, delete it immediately and issue a new key if necessary. Second, delete unused API keys right away. Keys that have not been used for a long time or are not expected to be used again should be deleted immediately from My Page to prevent the risk of a leak.
“A zero-tolerance approach”
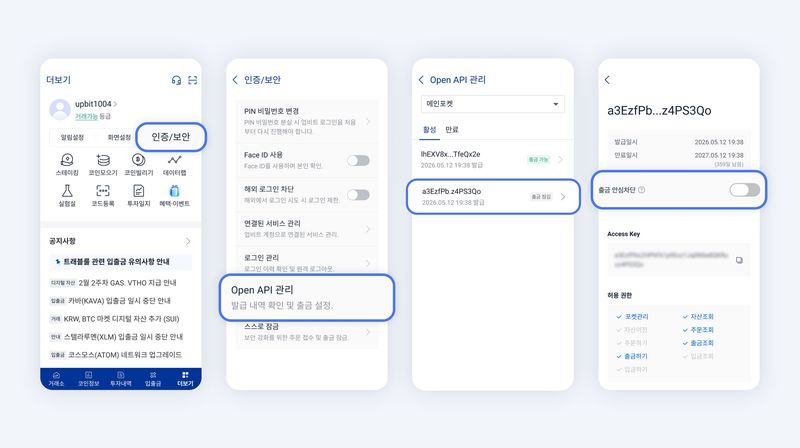
Dunamu Inc. is also strengthening API security to protect members from new types of scams, including the recent rise in quishing (QR code phishing). Withdrawals are blocked by default, even when an API key has withdrawal permission. This is a two-step safeguard: users can withdraw only after manually enabling the “Allow withdrawals” feature in the mobile app under “More - Security Authentication - Open API Management.” The app also supports KakaoTalk notifications when an API call is attempted from an IP address that has not been registered in advance. If an unusual request occurs that you do not recognize, check the IP address and access environment; if necessary, delete the relevant API key in the mobile app to protect your assets first.
Dunamu Inc. plans to take strong action against suspicious activities that harm members by touting unverified services or seeking other people’s accounts and API keys through false or exaggerated advertising. If such activity is detected, the company will immediately suspend member accounts used in the suspected activity or improperly lent, and request supporting materials. It also plans to respond with a zero-tolerance policy, including reporting cases to investigative authorities.
A Dunamu Inc. representative stressed, “Even if someone lures you with the claim that a key is only for simple lookups, handing your account information or API key to someone else is like placing the key to your own safe in the hands of a stranger.” The representative added, “Upbit will continue to put investor protection first and strengthen monitoring, doing its utmost to keep members’ assets safe from malicious scams.” Anyone who witnesses the improper lending of API keys or accounts, or suspicious recruitment activity, or suspects they have been affected, should report it to Upbit Customer Support as soon as possible.
[email protected] Han Yeong-jun Reporter