“A breach could spell disaster”: As GAs grow, defenses against hacking remain a blind spot
- Input
- 2026-10-20 16:22:13
- Updated
- 2026-10-20 16:22:13
According to the Korea Life Insurance Association on the 20th, as of August, agencies accounted for 50.9% (318,976 cases) of all new life insurance contracts (626,537 cases). That was about 10 percentage points higher than the 41.0% recorded in the same month three years earlier, in 2023. This is why large GAs are considered more influential than small and midsize insurers in insurance sales.
As GAs take on more than just selling insurance—handling everything from customer consultations to finalizing contracts—the volume of information they manage is also growing. Information that passes through GAs includes not only names and contact details but also sensitive insurance underwriting information, such as income and medical history.
The insurance industry, by contrast, sees their security systems as inadequate. With no uniform regulations for the GA industry, security is effectively left to each company’s discretion. Incar Financial Service, one of the very largest GAs, has just 1.6 information-security staff this year, far below the average of 25.9 in the financial and insurance industries.
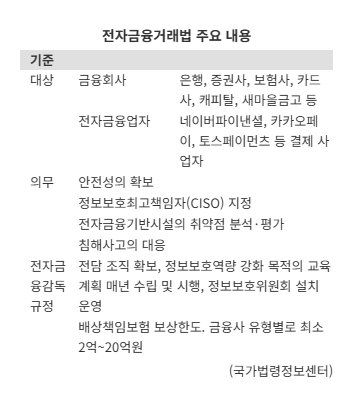
Accountability for financial incidents is also weak. The current Electronic Financial Transactions Act requires financial institutions and electronic financial business operators to designate a chief information security officer (CISO). They are tasked with ensuring security, analyzing and assessing vulnerabilities in electronic financial infrastructure, and responding to cyber incidents. But GAs are insurance agencies under the Insurance Business Act and are not subject to the Electronic Financial Transactions Act. As a result, they are not required to comply with detailed rules under the Electronic Financial Supervisory Regulations, such as maintaining dedicated teams for information-processing systems and electronic financial operations, developing and implementing training plans, or establishing and operating information security committees.
Efforts are nevertheless underway to raise security standards in the GA industry. In August, the Financial Security Institute launched an “Insurer-GA Information Security Council” to strengthen information-security capabilities. Following 14 GAs that joined last year, 11 more large GAs also became members of the institute in September this year. Insurers, however, argue that GAs should be brought under the Electronic Financial Transactions Act, given their scale—comparable to that of financial institutions—and the volume of information they handle. They also argue that regulations commensurate with that system should accompany efforts to establish a formal system for specialized insurance sales companies.
GAs, however, say the burden would be substantial. A GA industry official argued, “Since insurance agents make up most of the workforce, GAs have a different organizational structure from insurers. And given the wide size gap between large-scale GAs and other corporate entities, it would be impractical to bring them all under a uniform regulatory framework.”
There is also a counterargument that there is no particular reason to bring GAs under the Electronic Financial Transactions Act. The law’s applicability is determined not by a company’s size or the volume of personal information it handles, but by whether it processes payments through electronic payment instruments, among other things. On that basis, the argument goes, GAs have little connection to the law.
Securities firms are subject to the Electronic Financial Transactions Act regardless of their size because users make payments for transactions directly through the firms’ apps and similar platforms. Asset management firms and GAs, however, are excluded because customers do not directly access their systems to carry out electronic financial transactions such as transfers or payments.
A financial industry official said, “For large GAs, CISO appointments are also required under laws such as the Information and Communications Network Act,” adding, “Amending the Insurance Business Act or the Financial Consumer Protection Act could produce more practical regulatory results.”
[email protected] Kim Tae-il Reporter