Yoido Full Gospel Church and Sarang Church Hacked... Congregants’ Information and Offering Records Leaked on a Massive Scale
- Input
- 2026-10-06 22:18:55
- Updated
- 2026-10-06 22:18:55
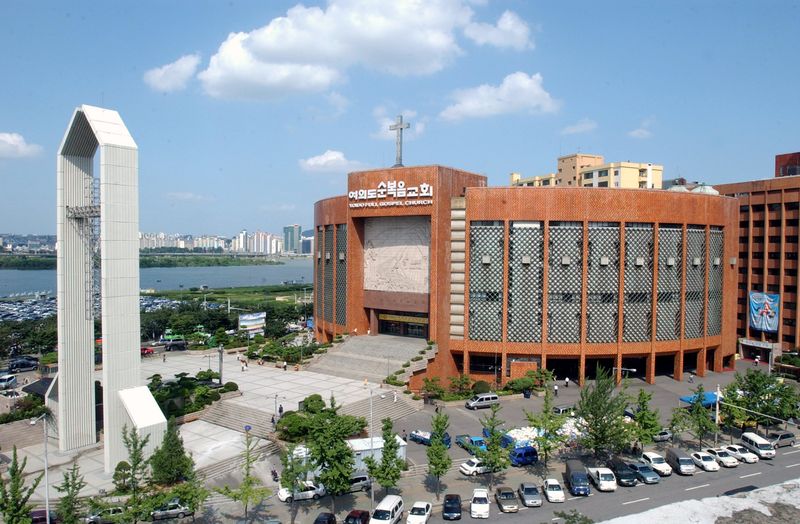
[Financial News] Signs have emerged that a cyberattack on Yoido Full Gospel Church and Sarang Church, two of South Korea’s largest churches, resulted in the large-scale leak of personal information, offering records, internal documents and other data belonging to nearly one million congregants. Both churches immediately formed emergency response teams (TFs) and began addressing the situation, including reporting it to the relevant authorities.
■ Yoido Full Gospel Church and Sarang Church targeted... Names, resident registration numbers and more stolen in bulk
On the 6th, cyber threat intelligence firm Oasis Security said that large amounts of evidence of system breaches and stolen data from two major South Korean churches had been found on servers used by overseas attackers. The targets were identified as Yoido Full Gospel Church and Sarang Church.
The analysis found that an attacker used a web shell (malicious software) to infiltrate Yoido Full Gospel Church’s enterprise resource planning (ERP) system and then obtained database administrator privileges. The overseas servers contained 47.3 GB of sensitive data, including about 960,000 records of congregant information updated over the past two years—such as names and resident registration numbers—which were recorded as having been stolen last August; 330,000 offering records; some 68,000 electronic approval documents; and some 14,700 internal messenger conversations.

Sarang Church’s groupware server was also found to have been breached using account credentials obtained in advance. The attacker exploited a vulnerability and used the single sign-on (SSO) function to extend access to the ERP system. The analysis found that names, addresses, phone numbers and other information belonging to 286 employees, including the senior pastor, and about 89,000 congregants had been stolen.
■ Churches: “Emergency security measures and TFs formed”... Congregants to be briefed at Wednesday worship services
After the Korea Internet & Security Agency (KISA) notified Yoido Full Gospel Church of signs of a suspected data leak, the church immediately began an emergency security review of the affected systems. The church said, “We are verifying the facts, and if a personal information leak is confirmed, we will respond swiftly and transparently in accordance with relevant laws and regulations.” It also plans to explain the situation and progress in its response directly to congregants at the upcoming Wednesday worship service.
Sarang Church has also acknowledged signs of a data leak, immediately formed an emergency response team (TF), and completed a report to the relevant authorities. It is focusing on preventing further damage.
■ U.S. religious platform accounts and possible use of AI... No connection to financial-sector hacks
Evidence has also emerged that administrator accounts and infrastructure obtained during a breach of a U.S. religious content and streaming service were used to target churches in South Korea. The possibility that artificial intelligence (AI) was used in the series of attacks has also been raised.
However, the security firm believes it is unlikely that the attacks were carried out by the same hackers behind the recent spate of cyberattacks on the financial sector, given the methods used. Oasis Security urged organizations to “conduct a comprehensive review of the connectivity and authentication and authorization systems of core business systems, including HR and accounting systems and groupware.”
[email protected] Park Ji-hyun Reporter