Yoon Ho-joong: “No AI-powered hacking attempts on government systems so far” [2026 parliamentary audit]
- Input
- 2026-10-06 18:46:07
- Updated
- 2026-10-06 18:46:07
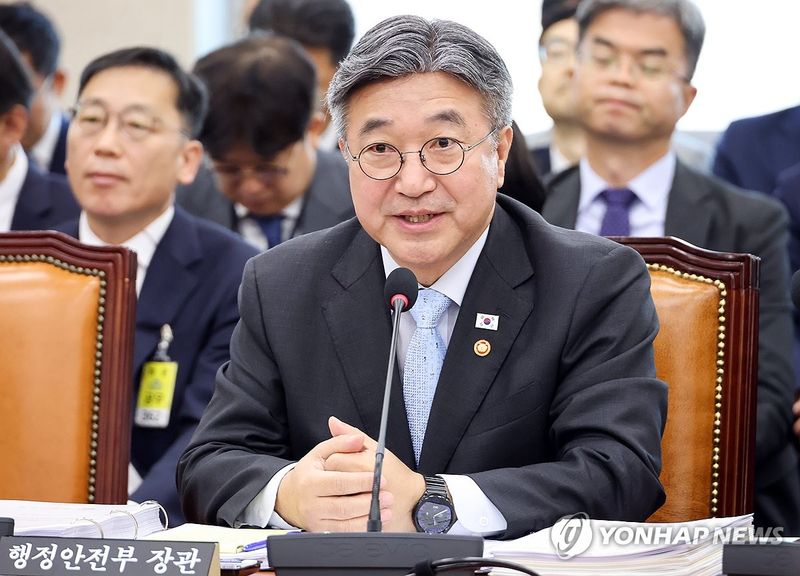
[Financial News] Interior and Safety Minister Yoon Ho-joong said on the 6th, “There have so far been no hacking attempts using artificial intelligence (AI) against any government systems.” As suspected AI-related data leaks have occurred repeatedly in the financial sector, interest has grown in the possibility of AI-driven hacking in the public sector as well. The government’s explanation is that no such attempts have been confirmed against government systems.
Minister Yoon made the remarks in a supplementary response during the Ministry of the Interior and Safety’s parliamentary audit by the National Assembly’s Public Administration and Security Committee. Cho Kuk Innovation Party lawmaker Jung Chun-saeng had asked whether the Government24 hack in August was carried out using AI or by a person.
Minister Yoon said, “The government network is completely separated from the general internet network under the network separation policy, and only a small portion is shared with the public.” He added, “Hacking attempts are mainly made against that portion, but I want to make clear that there have been no hacking attempts using AI so far.”
Earlier, Rep. Jung pointed out that the Ministry of the Interior and Safety had not provided sufficient notice that Government24 had been hacked and that no individual notifications had been sent. She also called for the government to prepare countermeasures against the possibility that AI-powered hacking could spread.
The webmail hacking incident at the Korea Local Information Research & Development Institute (KLID), an agency under the Ministry of the Interior and Safety, also came under scrutiny at the audit. The institute’s webmail was recently hacked, and about 6GB of data was stolen. Democratic Party of Korea lawmaker Lee Kwang-hee pointed out that the institute had left in place vulnerable software that should have been removed when it set up its email system in 2018, and that hackers exploited the software eight years later.
In response, KLID President Woo Jeong-min said, “I believe this is the period when information security is most vulnerable.” He added, “The institute also operates important systems, so we established an Information Planning Group reporting directly to senior executives.” He went on to say, “We plan to conduct vulnerability checks on an ongoing basis.”
[email protected] Lee Bo-mi Reporter