"Cannot Rule Out AI Use"... Financial Authorities Adopt Highest-Level Emergency Response Posture Against Cyberattacks
- Input
- 2026-10-04 16:05:04
- Updated
- 2026-10-04 16:05:04
[Financial News] Following a series of personal-information breaches in the financial sector since Sept. 30, financial authorities called in relevant government agencies, as well as the heads of financial-sector associations and organizations, and urged them to exercise "exceptional vigilance." After receiving notice of Shinhan Bank's breach, the authorities promptly launched an on-site investigation that same day and are closely examining the cause and scope of the damage. With vulnerabilities emerging even in conventional cyberattacks, rather than attacks involving AI at the level of Claude Mythos, the financial sector as a whole has entered an emergency response posture.
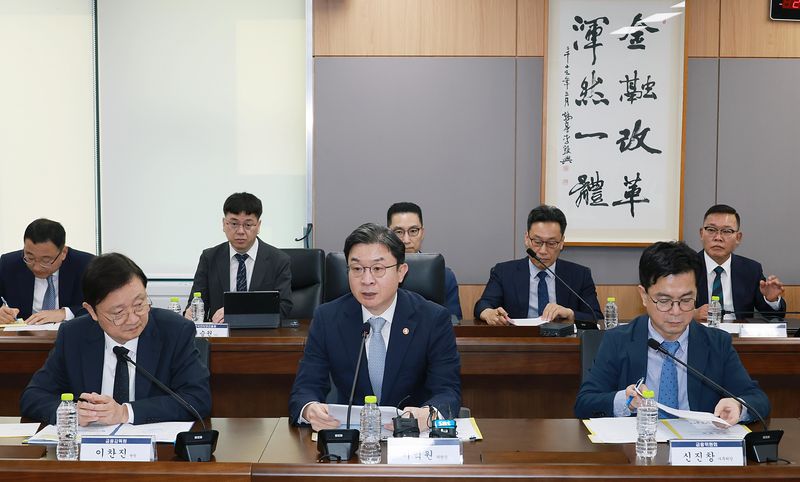
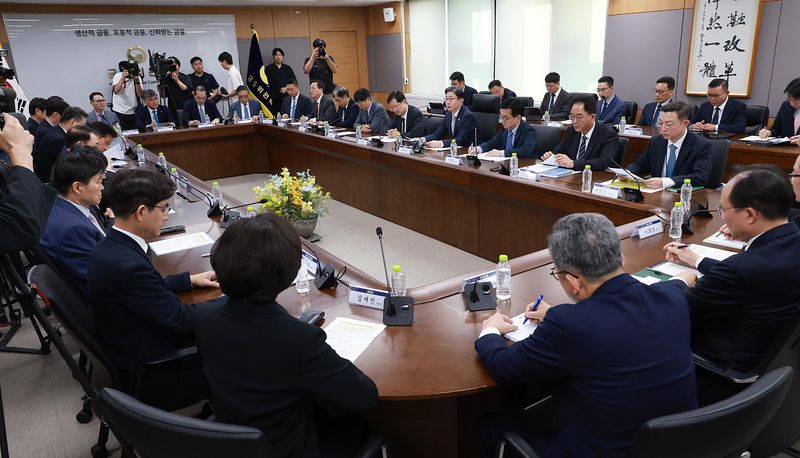
On the 4th, Lee Eok-won held an "Emergency Inspection Meeting for the Entire Financial Sector" to address recent cyber threats facing the financial sector, with the Financial Supervisory Service, Financial Security Institute, associations for each financial sector, and major financial companies in attendance. To establish a cooperative framework among relevant ministries, the FSC also invited the Ministry of Science and ICT, the Personal Information Protection Commission (PIPC), and the Korean National Police Agency. The FSC said it organized the meeting because signs indicated that cyberattacks on major financial companies had occurred in succession. It aimed to share information on financial companies' data-breach incidents, attack types, and methods, and to ensure that the entire financial sector responds with exceptional vigilance to prevent further breaches and harm to the public.
Lee said, "As breach threats have spread throughout the financial sector, I ask that the following measures be implemented thoroughly, based on the understanding that the entire financial sector will respond jointly to prevent unnecessary anxiety in advance while protecting consumers."
He urged them. The FSC instructed financial institutions to take every precaution to prevent breaches by thoroughly inspecting external-facing interfaces and intrusion-activity detection systems so that consumers can use financial services with confidence. As instructed at the emergency situation-response meeting on Oct. 2, institutions must identify all externally exposed IT assets and services and conduct a comprehensive recheck of security vulnerabilities, authentication and access controls, and intrusion-activity detection systems. Accordingly, the entire financial sector—including banks and card companies, as well as mutual finance institutions, savings banks, insurers, securities firms, fintech companies, and small and midsize financial companies—must promptly complete its self-inspections and report the results to the FSC and Financial Supervisory Service.
The FSC instructed each financial company to properly incorporate already circulated threat intelligence—including attack IP addresses, attack methods, records of intrusion attempts, and incident cases—into its detection and blocking systems. The aim is to prevent attacks by hackers using AI agents from spreading widely. In particular, institutions were ordered to check whether known vulnerabilities had been patched promptly. The government said it would respond strictly if financial companies had neglected necessary inspections and countermeasures despite already-shared attack information and incident cases.
The routes through which cyberattacks can infiltrate will be blocked as much as possible. Regardless of whether they are connected to customer-facing services, all external-facing interfaces and system access routes used by employees and others for work will be identified and inspected to minimize potential risks. As a rule, all external access will be blocked except where it is indispensable for providing consumer services or performing business operations. Even when external access is unavoidable for work, access privileges and the information available for viewing will be limited to the minimum necessary.
The FSC stated, "Financial institutions must ensure that personal credit information is not unnecessarily stored or accessed in systems used by outside personnel, such as loan solicitors and contractors, or by employees. They must also thoroughly check whether there are any routes through which authentication procedures could be omitted or bypassed."
Financial companies that experienced breaches were ordered to take prompt protective measures. They must quickly and accurately determine the scope of the leaked information and the possibility of consumer harm, and immediately implement necessary safeguards to prevent further data leaks or financial losses. If consumer harm is confirmed, consumers are expected to be notified of the details and provided with remedies and compensation. The financial authorities also ordered institutions to prepare thoroughly for possible secondary harm, such as voice phishing and smishing exploiting leaked information, and to strengthen necessary preventive measures, including detecting abnormal financial transactions and informing consumers.
Lee said, "As financial digitalization and links between services provided by financial companies expand, the possibility that a security vulnerability at one financial company could develop into a risk for the entire financial sector is also growing. The entire financial sector must use this incident as an opportunity to reexamine its overall information-security systems from the ground up, approach the matter with extraordinary resolve and the highest level of vigilance, and raise its security standards by one level." He continued, "We will swiftly and clearly determine the nature of the breach threats through investigations into the causes of the incidents that have occurred, and closely guide and supervise whether the consumer-protection measures prepared by financial companies are being implemented thoroughly." He added, "We will mount an all-out response to prevent harm to the public caused by breach incidents from occurring and spreading by closely analyzing recent types of breach incidents and patterns of damage and actively identifying necessary institutional-improvement tasks."
Lee said, "While it is difficult to say definitively, the possibility of hacking attacks using AI cannot be ruled out," adding, "Regarding the exact causes and attack methods of individual incidents at present,
more thorough investigation and analysis are needed," he added.
[email protected] Park Moon-soo Reporter